Ghost Credentials: How Forgotten Access Badges Quietly Become Your Facility's Most Exploitable Weakness
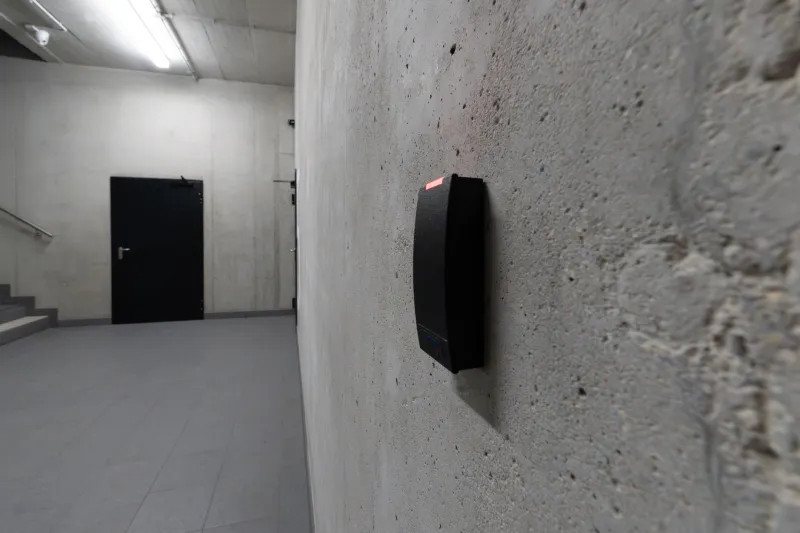
The Badge That Nobody Canceled
Somewhere in your organization right now, there is a former employee who still holds a valid access credential to your facility. You probably don't know who they are. Your front desk staff almost certainly doesn't. And depending on how your access control system is configured, neither does the software managing it.
This is not a hypothetical. It is the operational reality for thousands of businesses across the United States, from small commercial offices to large industrial campuses. Organizations acquire access credentials at a predictable rate—every new hire, every contracted vendor, every consultant brought in for a six-week engagement—but they retire those credentials inconsistently, if at all. The result is what security professionals sometimes call "credential creep": a slow, invisible accumulation of active badges attached to individuals who no longer have any legitimate claim to your building.
The consequences of this accumulation are not theoretical. They are documented, recurring, and frequently devastating.
How Credential Creep Develops
Understanding why this problem persists requires looking at the organizational dynamics that produce it. Access badge issuance typically involves multiple departments—human resources, facilities management, IT, and sometimes individual department heads—but badge deactivation rarely has a clear, singular owner. When an employee leaves, HR may process the paperwork, but if the access control system lives under facilities or IT, the notification chain breaks down. The badge gets surrendered at the front desk, or it doesn't, and the credential itself remains active in the system regardless.
Contractors and consultants create an even more fragmented picture. A vendor brought in to service HVAC equipment may receive a temporary badge for a two-day job. If that badge is not physically collected and digitally deactivated upon departure, it remains a functional key to your facility indefinitely. Multiply this across dozens of vendor relationships over several years, and the scope of the problem becomes difficult to overstate.
Mergers and acquisitions compound the issue further. When one organization absorbs another, it frequently inherits not only the physical access infrastructure but the entire legacy credential population of the acquired company—individuals who may have left years before the acquisition but whose badges were never purged from the system.
Real-World Consequences
The security industry has documented numerous cases where dormant credentials enabled unauthorized access to commercial and institutional facilities. In several high-profile cases involving financial services firms, former employees used retained access badges to reenter facilities after their termination—in some instances, during active litigation with their former employer. In healthcare settings, unauthorized access by individuals holding expired contractor credentials has created significant HIPAA exposure, triggering regulatory investigations that extended well beyond the initial security breach.
Perhaps most instructive are the cases where credential misuse went undetected for extended periods. Because access control logs are often voluminous and rarely reviewed in real time, a former employee using a valid badge can move through a facility without triggering any immediate alert. The badge works. The door opens. The log records the entry as legitimate. Nobody is notified. The intrusion is only discovered—if it is discovered at all—during a retrospective audit triggered by an unrelated incident.
This is the insidious nature of ghost credentials: they don't announce themselves. They operate within the normal parameters of your access control system because, as far as the system is concerned, they are normal.
Building an Access Control Audit Framework
Reclaiming control of your credential landscape requires a structured, cross-departmental approach. The following framework is designed to be implemented in phases, allowing organizations to prioritize the highest-risk categories of dormant credentials while building toward a comprehensive inventory.
Phase One: System Enumeration
Begin by extracting a complete list of every active credential in your access control system. This list should include the credential identifier, the name associated with it, the date it was issued, the access level it carries, and the date it was last used. Many organizations are surprised to discover that their access control software can produce this report but that no one has ever requested it.
Cross-reference this list against your current HR roster. Any credential associated with an individual who does not appear on the active employee list should be flagged for immediate review.
Phase Two: Contractor and Vendor Reconciliation
Compile a separate inventory of credentials issued to non-employees. For each credential, identify the associated vendor relationship, the original purpose of access, and the expected duration of that access. Credentials issued to vendors whose contracts have expired or whose service engagements concluded more than 90 days ago should be deactivated immediately, pending any documentation of an ongoing relationship.
Phase Three: Access Level Validation
For credentials that survive the first two phases, evaluate whether the access level assigned to each credential still reflects the holder's current role and operational need. Credential creep is not only about volume—it is also about scope. An employee who transferred from a sensitive operations role to an administrative position three years ago may still carry an access level that grants entry to areas they no longer need to enter.
Phase Four: Automated Deactivation Protocols
Work with your IT and facilities teams to configure automated deactivation triggers within your access control system. At minimum, credentials should be automatically suspended upon HR notification of separation, and contractor credentials should carry a built-in expiration date tied to the contract term. Automation does not eliminate the need for manual review, but it closes the most common gap: the lag between a personnel change and a system update.
Phase Five: Ongoing Audit Cadence
Schedule a full credential audit on a minimum semi-annual basis. Assign clear ownership for this process—preferably a named individual in a security or facilities role with the authority to deactivate credentials without requiring multi-departmental approval. The longer the approval chain, the more likely the deactivation is to be delayed or forgotten.
The Organizational Discipline Required
Credential audits are not a one-time remediation. They are an ongoing operational discipline that requires sustained organizational commitment. The most rigorous access control technology available will not protect a facility if the processes governing credential issuance and retirement are poorly maintained.
For organizations that lack the internal capacity to manage this discipline independently, partnering with a professional security provider that includes access control management as part of its service offering can bridge the gap. Experienced security professionals bring both the technical fluency to navigate complex access control systems and the operational perspective to identify vulnerabilities that internal teams—often too close to the day-to-day workflow—may overlook.
Your facility's first line of defense is knowing exactly who has permission to be inside it. Until your credential inventory reflects your actual population of authorized individuals, that defense has a gap in it—and gaps, in security, are never neutral.